BitLocker Asking for Recovery Key After a BIOS Update? How to Fix It
You update the BIOS or UEFI firmware on a Windows 11 PC, restart, and unexpectedly see the blue BitLocker recovery screen. Instead of starting Windows, the computer asks for a 48-digit recovery key.
This can happen because BitLocker uses hardware and boot measurements to protect encrypted data. A firmware or TPM-related change can cause Windows to request proof that you are authorized to unlock the system drive.
Quick answer:
- Note the recovery key ID on the blue screen, retrieve the matching 48-digit key from the Microsoft account or your organization's management system, and enter it. Once back in Windows, investigate any repeated prompts before performing additional firmware changes.
- Why Does a BIOS Update Trigger BitLocker Recovery?
- Part 1: Read the Recovery Key ID on the Blue Screen
- Part 2: Find Your 48-Digit BitLocker Recovery Key
- Part 3: Enter the Correct Key and Start Windows
- Part 4: What If BitLocker Asks for the Key on Every Restart?
- Part 5: Prevent Recovery Prompts Before Future BIOS Updates
- What If You Cannot Find the Recovery Key?
- Can iSumsoft BitLocker Reader Help?
- Frequently Asked Questions
- Conclusion
- Sources
Why Does a BIOS Update Trigger BitLocker Recovery?
BitLocker protects an encrypted Windows volume using mechanisms that can include the Trusted Platform Module (TPM) and boot configuration measurements. When a BIOS/UEFI, Secure Boot, or TPM change alters expected measurements, automatic unlocking may be interrupted and recovery authentication may be required.
A recovery prompt does not necessarily mean the BIOS update failed or that files were deleted. It also does not mean BitLocker can be bypassed without a valid recovery mechanism.
Microsoft describes firmware-triggered recovery and the importance of suspending BitLocker for certain planned updates in its BitLocker recovery known issues documentation.
Part 1: Read the Recovery Key ID on the Blue Screen
Do not reset Windows or clear the TPM in an attempt to dismiss the screen.
Step 1 Leave the PC powered on at the BitLocker recovery prompt.
Step 2 Find the Recovery key ID displayed on the screen.
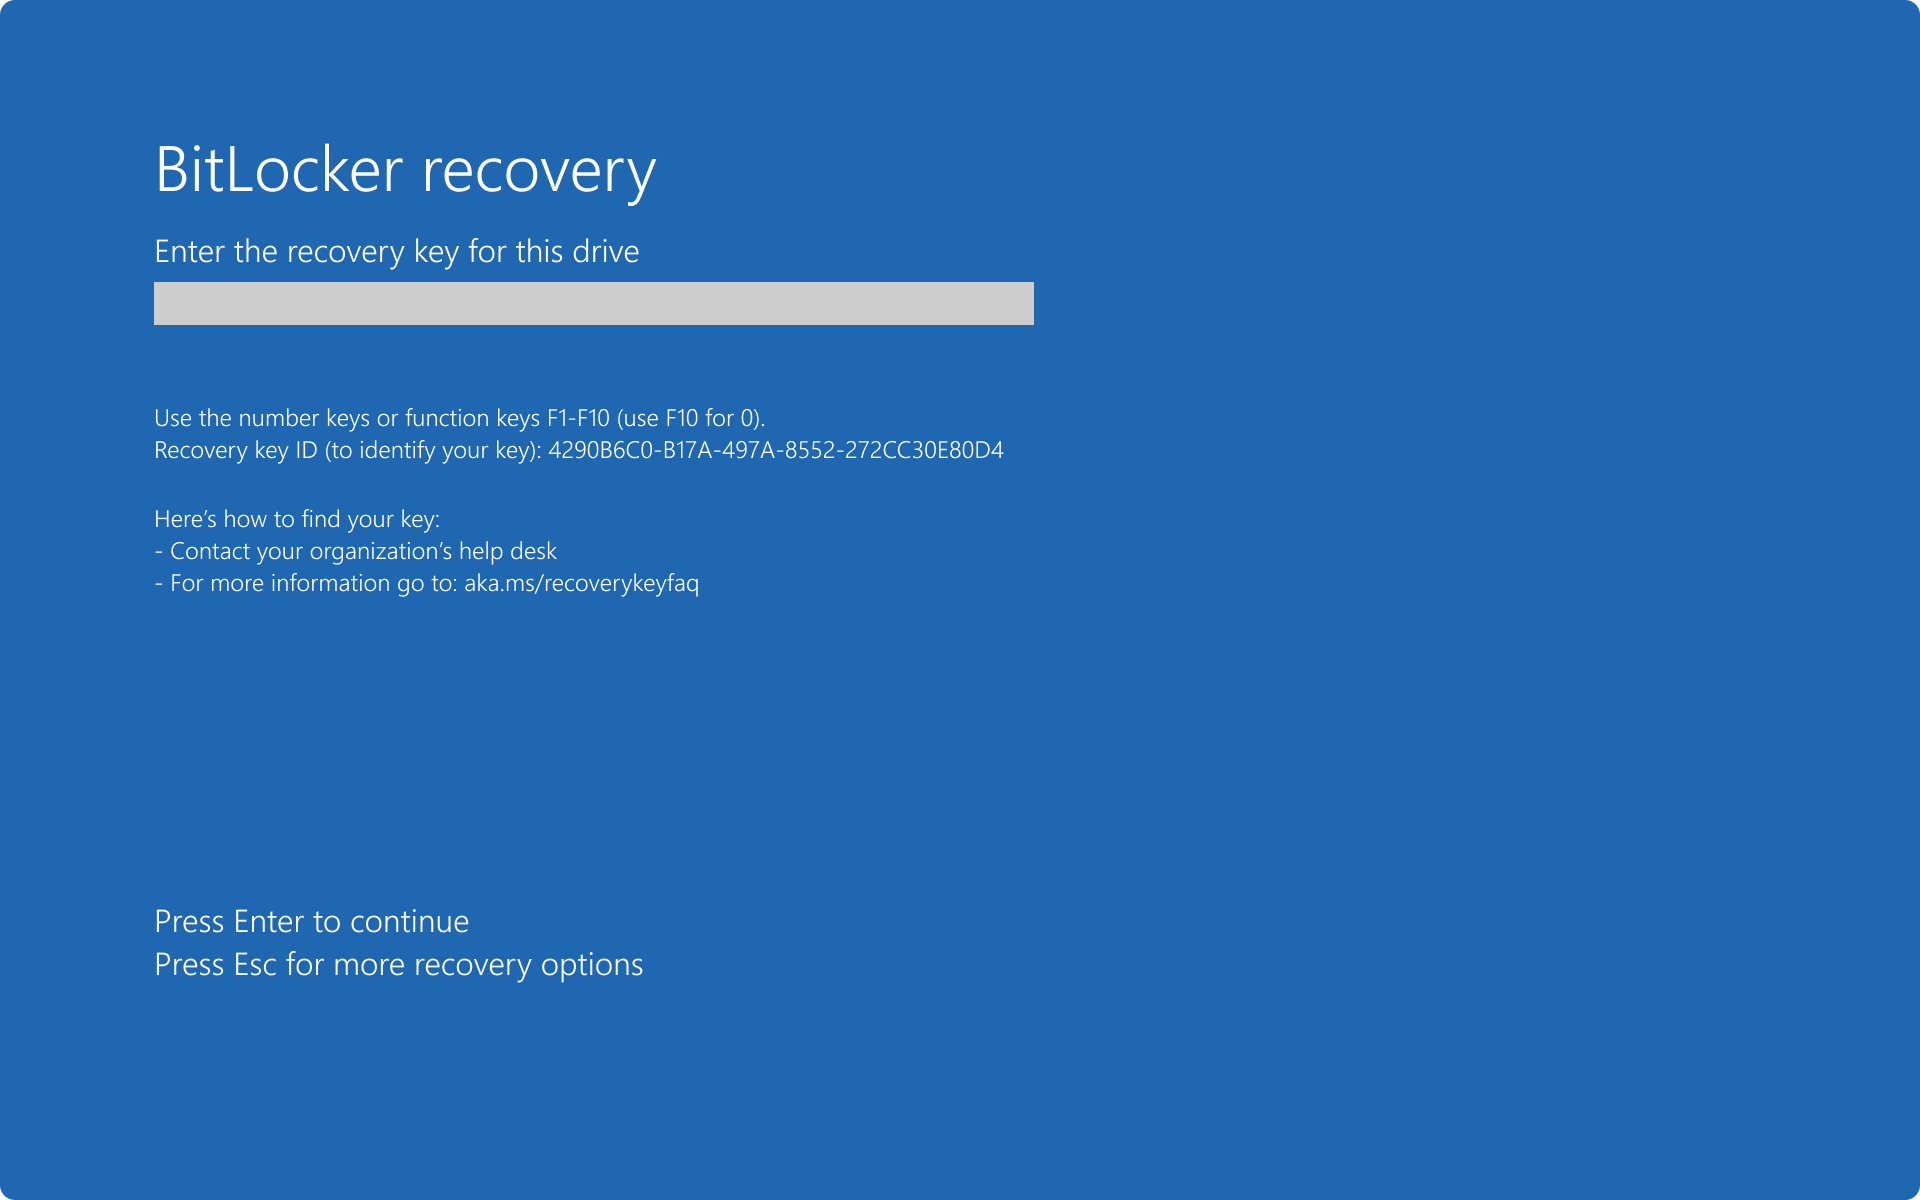
The Recovery key ID helps you identify the matching key. Do not photograph or share the complete 48-digit recovery key.
Step 3 Write down or photograph the ID, not the complete recovery key.
Step 4 If multiple keys are stored in your account, the ID will help match the correct one.
Part 2: Find Your 48-Digit BitLocker Recovery Key
Option A: Personal Microsoft account
Step 1 From another device, open https://aka.ms/myrecoverykey.
Step 2 Sign in with the Microsoft account associated with this computer.
Step 3 Compare the Key ID in the account with the one shown on the locked PC.

Existing iSumsoft example of an older Microsoft account page. Match the Key ID on your own device; the account layout may differ.
Step 4 Use the corresponding 48-digit recovery key to unlock the drive.
Option B: Work or school account
If the computer belongs to your employer or school, the key may be stored in an organization-managed account. Visit https://aka.ms/aadrecoverykey if your organization permits self-service recovery, or contact IT with the displayed key ID. Do not post any full key publicly.
Option C: Printout, saved text file, or USB drive
Look for a recovery-key printout or file created when BitLocker was enabled. Some users save it separately on a USB drive. Match the identifier before entering the key.
Microsoft's official guide explains all these possibilities: Find your BitLocker recovery key.
Part 3: Enter the Correct Key and Start Windows
Step 1 Carefully enter the matching 48-digit recovery key at the blue prompt.
Step 2 Confirm the entry and wait for the PC to continue starting.
Step 3 Sign in to Windows normally.
Step 4 Save a securely managed copy of the key for future recovery events.
Step 5 If this is a corporate device, report the incident to your IT administrator.
If the key is rejected, verify that the key ID matches. A device can have multiple recovery-key records or have been re-encrypted during its lifetime.
Never send a recovery key to a random support contact or paste it into a public forum.
Part 4: What If BitLocker Asks for the Key on Every Restart?
A one-time recovery after a firmware change is different from a prompt that returns after every boot. Repeated prompts require investigation.
Check these conditions in order:
Firmware update completed: Review your computer manufacturer's BIOS revision notes and installed version. Do not flash an older BIOS as a guess.
Unexpected boot changes: Check for recently changed boot order, external boot devices, or Secure Boot configuration. Do not toggle security features blindly.
TPM state: Open tpm.msc after Windows starts to inspect TPM status. Do not clear the TPM to troubleshoot a recovery screen without specific manufacturer or administrator guidance and confirmed keys.
Windows updates: Apply appropriate official updates after confirming your device model and firmware compatibility.
BitLocker protection status: In an elevated Command Prompt, run the following read-only command:
manage-bde -status C:On a managed computer, ask IT to review BitLocker and TPM event logs. Repeated recovery might indicate an unresolved firmware or security measurement problem; there is no universal single-click repair.
Part 5: Prevent Recovery Prompts Before Future BIOS Updates
When the manufacturer or administrator instructs you to install firmware that could trigger BitLocker recovery, the recommended sequence is:
Step 1 Make sure you have a valid and securely stored recovery key.
Step 2 Save your work and connect the laptop to AC power.
Step 3 Review your device manufacturer's firmware update instructions before starting the installer.
Step 4 If instructed for your setup, temporarily suspend BitLocker protection before starting the update.
Step 5 Complete the firmware installation and all restarts.
Step 6 Resume BitLocker protection and verify its status afterward.
Microsoft documents a PowerShell method for authorized administrators:
After securely saving the recovery key, suspend protection in an elevated PowerShell window:
Suspend-BitLocker -MountPoint "C:" -RebootCount 0After the firmware update and all required restarts, resume protection:
Resume-BitLocker -MountPoint "C:"Warning:
-RebootCount 0suspends protection until it is explicitly resumed. Do not leave the device in that state. For ordinary users, the Windows BitLocker management interface or manufacturer-provided update process may be safer than running commands. On managed devices, follow IT policy instead of changing BitLocker yourself.
What If You Cannot Find the Recovery Key?
Microsoft cannot recreate a lost recovery key. Check all accounts that could own the device, work/school management records, printed records, and USB files. If a different person originally configured the device, the key may belong to that person's account.
Without a valid recovery method, the encrypted files cannot simply be unlocked by third-party software. Resetting or reinstalling Windows can remove existing data. Do not choose a destructive recovery option until you accept its consequences.
Can iSumsoft BitLocker Reader Help?
iSumsoft BitLocker Reader is intended for managing and accessing supported BitLocker-encrypted data volumes. Its user guide describes unlocking a supported drive with a valid password or recovery key.
It cannot bypass a locked Windows system drive at pre-boot recovery or generate a missing 48-digit key.
Frequently Asked Questions
Does a BIOS update remove my BitLocker recovery key?
Not necessarily. The update can trigger an additional authentication check. Your key may still be available in your Microsoft account or organization-managed records.
Can I press Esc to bypass the BitLocker screen?
An alternate menu may appear, but that does not decrypt the drive. Unlocking the encrypted volume requires a legitimate protector or recovery mechanism.
Should I disable Secure Boot to stop BitLocker recovery?
No. Changing Secure Boot settings may itself trigger further recovery and weaken security. Use the manufacturer's official guidance.
Should I clear TPM after a BIOS update?
Not as a routine troubleshooting step. Clearing TPM can affect protected keys and access to encrypted data.
Can BitLocker Reader unlock my Windows drive without the recovery key?
No. The product requires a valid unlocking credential for supported encrypted data drives and is not a pre-boot system-drive recovery bypass.
Conclusion
A BitLocker recovery prompt after a BIOS update is usually a security verification event, not evidence that all your files are gone. Identify the key ID, retrieve the matching 48-digit recovery key, unlock Windows, and then investigate recurring recovery prompts. Before future firmware updates, verify the key and follow the appropriate BitLocker suspension and resumption procedure.
Sources
- Microsoft: Find your BitLocker recovery key
- Microsoft: BitLocker recovery known issues
- iSumsoft BitLocker Reader limitations
See Microsoft Suspend-BitLocker and Resume-BitLocker for command behavior.